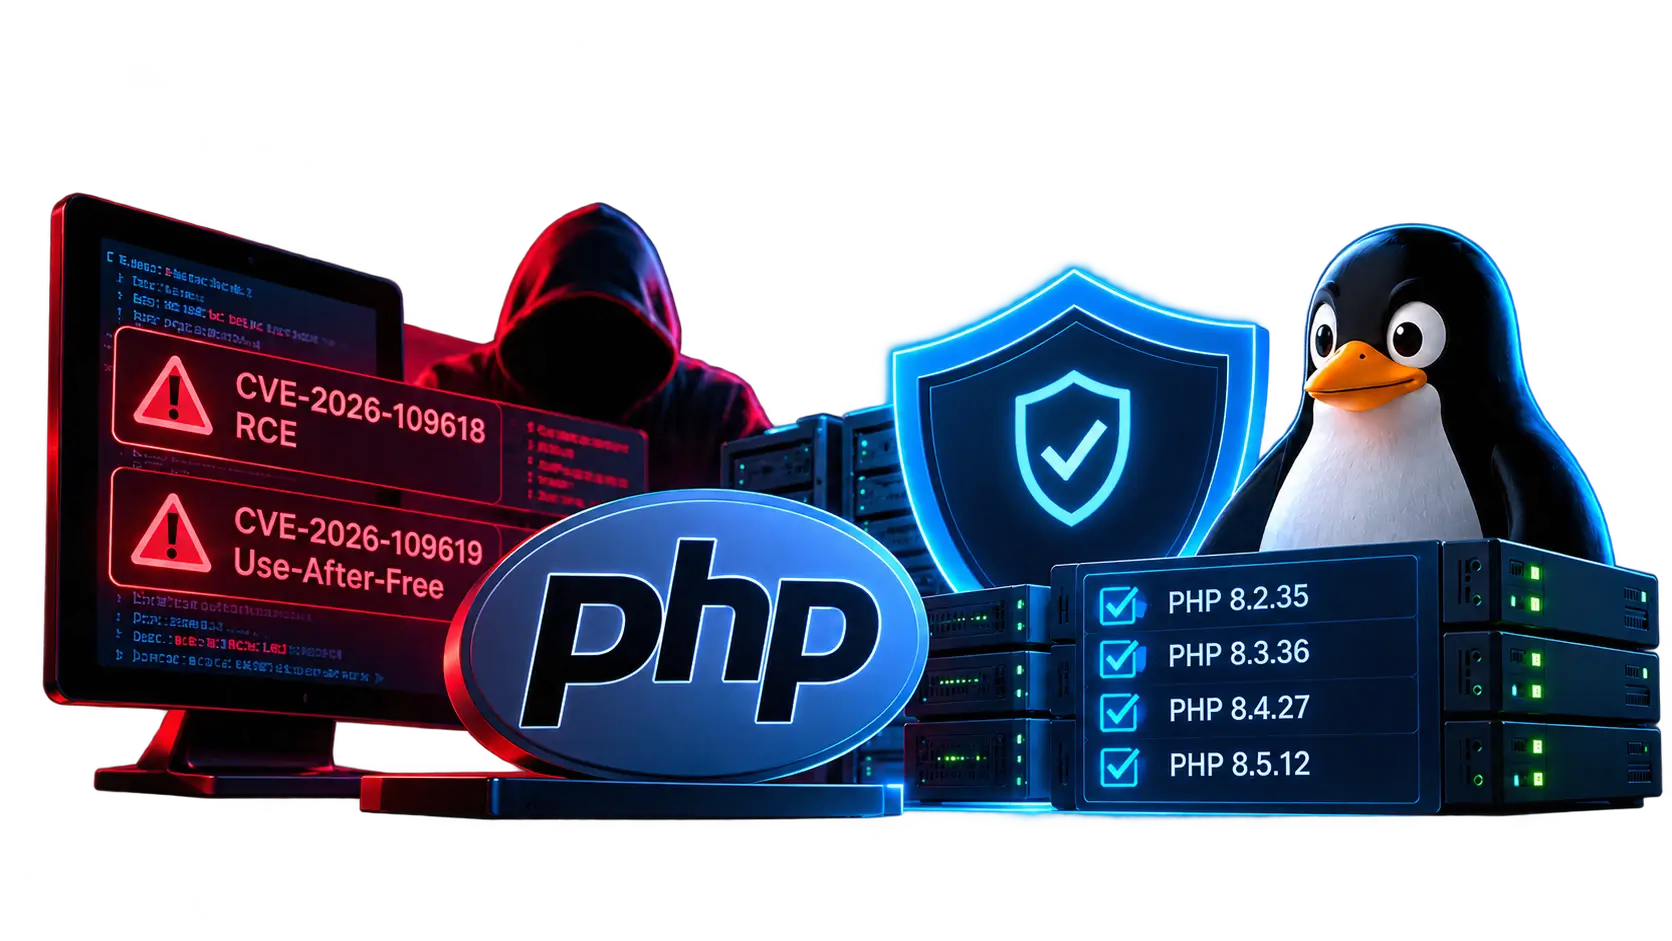
Two critical vulnerabilities have been discovered in PHP — CVE-2026-109618 and CVE-2026-109619. They involve memory handling errors and, under certain conditions, allow an attacker to execute unauthorized code on the server. Updating a CMS or its plugins is not enough: PHP itself needs to be patched.
We previously explained why regular PHP updates are important and the risks of running unsupported versions. This incident has once again shown why security updates should not be postponed.
Our hosting platform uses extended PHP support from TuxCare, which provides security fixes, including for older PHP branches covered by the service. This is particularly important for websites that cannot yet move to a newer PHP version without code changes and compatibility testing.
With the available patches and our team’s prompt response, the necessary updates have been installed across our hosting platform. Both vulnerabilities have been fixed. Extended support helps address these threats promptly, but it does not eliminate the need for planned website modernization.
Both affected websites have been restored
Two clients’ websites were compromised during the incident. We promptly detected the issue, restored the websites from backups, and installed the necessary patches.
The maximum downtime was 20 minutes. Both websites are now operational. Backups enabled us to restore availability quickly, while the PHP updates addressed the identified vulnerabilities in the server environment.
Обговорення
0 коментарів
Коментарів поки немає.
Додати коментар
Щоб залишити коментар, увійдіть до облікового запису або зареєструйтеся.